Public procurement spending in Sweden amounted to SEK 1,009 billion in 2023, corresponding to 18.4 percent of GDP. Because of this, public procurement affects not only the economy and organizational development, but also society’s ability to manage disruptions, cyberattacks, and geopolitical change.
When a public organization purchases a mission-critical system, it is not only choosing functionality and price. It is also choosing future supplier dependencies, security risks, and freedom of action.
Procurement Determines Future Resilience
Cybersecurity is often associated with firewalls, encryption, monitoring, and technical security solutions. However, many decisive security decisions are made much earlier, when an organization chooses which systems, platforms, and suppliers it will use.
A contract may remain in force for many years. During that time, the threat landscape may change, suppliers may be acquired, subcontractors may be replaced, and new geopolitical or regulatory risks may emerge. Dependencies built into the procurement may therefore affect continuity, security, and digital freedom of action long after the contract has been signed.
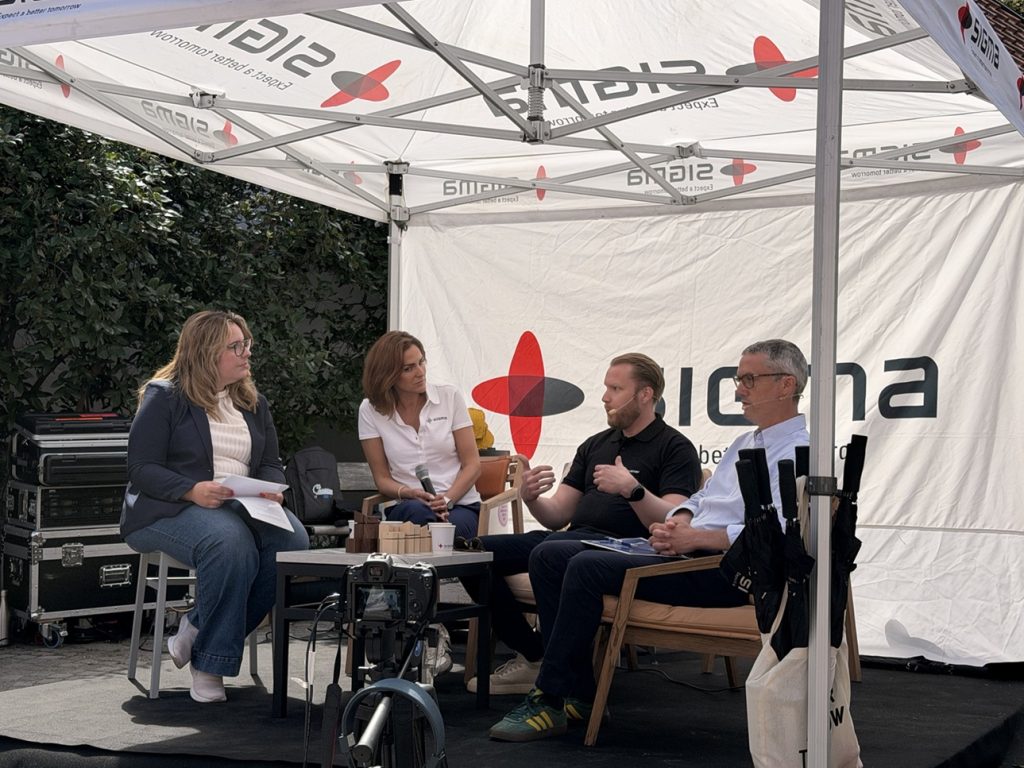
The issue was a central topic during Sigma Technology Tech Talks at Almedalen Week 2026. The discussion featured David Nordström, CFO of cybersecurity company Clavister, Viktor Morawski, Head of Procurement at Botkyrka Municipality and board member of the Swedish Association of Public Purchasers, and Vlora Ramadani, CEO of Sigma Technology North Solutions. Bidding expert Anna Nyblin moderated the discussion.
The panel discussed how public procurement can be used not only to purchase technology, but also to strengthen Sweden’s security, preparedness, and long-term resilience.
Preparedness Begins Before the Crisis Occurs
The pandemic, the war in Ukraine, and the changing security environment have highlighted just how dependent society is on functioning supply chains.
Viktor Morawski described how preparedness has become an increasingly important aspect of procurement work:
“We are beginning to think about what our supply chains look like. How can we design our procurements so that we are not as vulnerable if a new pandemic or another crisis occurs?”
Just as preparedness for food, pharmaceuticals, and energy must be established before a crisis occurs, digital resilience must be planned in advance. When a disruption has already become reality, it is often too late to discover that the organization lacks alternative suppliers, access to its data, or the ability to switch technical platforms.
As David Nordström put it:
“What we specify as requirements in peacetime represents our maximum capability in wartime.”
This makes continuity, redundancy, and recovery capability central procurement issues, not merely technical matters for the IT department.
Supplier Dependencies are Also Cyber Risks
Cyber risk is not solely about the likelihood of a technical intrusion. It is also about which suppliers, subcontractors, platforms, and jurisdictions an organization becomes dependent upon.
Before a critical digital procurement, an organization therefore needs to understand:
where sensitive and mission-critical data is stored
which subcontractors are part of the delivery
which legislation applies to the supplier and its subcontractors
how dependent the organization becomes on a particular platform or competence
what happens if the supplier can no longer deliver or is no longer permitted to deliver
how data, integrations, and processes can be migrated to another solution
David Nordström emphasized the importance of understanding both data and the legal environment surrounding it:
“Where do I have highly sensitive data? Where do I have personal data? Where do I have classified information? Which legislation do I trust the most?”
These questions become particularly important in critical societal functions, where a prolonged outage may affect far more than a single organization.
Digital Sovereignty is About the Ability to Act
Digital sovereignty can be described as the ability of an organization, country, or region to retain control over critical digital functions, data, and technical infrastructure.
This does not mean that all technology must be developed or operated locally. Nor does it mean complete technological self-sufficiency. However, digital sovereignty does require organizations to understand and actively manage their dependencies.
In practice, this may involve:
knowing where critical data is stored and processed
mapping suppliers and subcontractors
assessing legal and geopolitical risks
avoiding unnecessary vendor lock-in
creating realistic alternatives if a supplier disappears
ensuring that critical operations can continue during major disruptions
During the discussion, David Nordström highlighted how other regions use public procurement as a strategic opportunity to stimulate research and development by creating a competitive environment. In China, all public procurement within strategic sectors favors Chinese companies. In the United States, this share is estimated at 70 percent. By comparison, in some EU member states only 8 to 12 percent of public procurements are awarded to European suppliers.
Public procurement thus becomes a tool for translating digital sovereignty from a political ambition into practical risk management.
"If we want to maintain communications capability within key sectors of our society and reduce our dependence on third countries, then we must consider what redundancy we need to build." David Nordström, CFO, Clavister
Resilience Requires Alternatives, but Also Manageability
A common response to increasing cyber risks is to introduce more requirements, controls, and regulations. That is important, but resilience is not created solely through stricter security requirements. Organizations must also have realistic courses of action.
A strong dependence on a single supplier or platform can create concentration risk. At the same time, too many suppliers may result in more integrations, less clear accountability, and a larger attack surface.
The goal should therefore not be maximum supplier diversification, but a deliberate balance between diversification, security, and manageability.
This may include:
dividing large contracts when appropriate
ensuring that critical expertise does not reside with a single provider
using open standards and documented interfaces
requiring transparency in relevant subcontractor chains
planning how a supplier replacement would be carried out in practice
distinguishing between desirable redundancy and unnecessary complexity
Security Requirements Must not Exclude Innovation
Smaller and specialized companies can contribute innovation, cutting-edge expertise, and alternative solutions. However, many choose not to participate in public procurement because the processes are perceived as overly burdensome or the requirements as disproportionate.
“A significant share of innovation and specialist expertise resides in smaller companies. But if procurements are designed so that only the largest companies can participate, the public sector risks missing out on both new solutions and valuable expertise. Requirements should certainly be demanding, especially regarding security, but they must also be relevant and proportionate. Otherwise, many smaller companies opt out of the procurement process from the very beginning, a pattern we have observed for many years.” Vlora Ramadani, President at Sigma Technology North Solutions
This does not mean lowering security requirements. Rather, requirements should be relevant, proportionate, and linked to actual risk.
Early market dialogues, functional requirements, and dividing procurements into smaller lots can, in certain procurements, enable more qualified suppliers to participate. This can strengthen competition and innovation without compromising security.
The New Cybersecurity Act Strengthens Responsibility
The Swedish Cybersecurity Act, which implements the EU NIS2 Directive, has been in force since January 15, 2026. The legislation imposes clearer requirements regarding risk management, security measures, incident reporting, and management participation in cybersecurity efforts. The regulation raises the baseline, but compliance is not the same thing as actual resilience.
An organization may comply with formal requirements while still being highly dependent on a single supplier, lacking a realistic exit plan, or having limited insight into its supply chain. Procurement, IT, security, legal, and business management functions must therefore collaborate as early as the needs-analysis phase.
Cybersecurity cannot be added as a separate package of requirements at the end of a procurement process. It must be incorporated into the design of the engagement from the very beginning.
Five Questions Before the Next Critical Digital Procurement
Ensure that data can be exported, integrations are documented, and the organization has rights to the necessary information and expertise during a supplier transition.
An exit plan should describe responsibilities, costs, timelines, data transfer, and how operations will continue during the transition. The plan should also be tested and followed up throughout the contract period.
From Compliance to Real Resilience
If the public sector wants to change its purchasing patterns, clear and long-term priorities are required.
Viktor Morawski emphasized the need for a shared direction:
“If you want a different type of purchasing pattern, you must be clear: this is how we want it, and we are aligned on that politically.”
Cybersecurity is therefore no longer solely an issue for the IT or security department. It is a management issue and a central part of strategic procurement.
Organizations that map their digital dependencies, create realistic alternatives, and define requirements for continuity are better prepared when the next disruption occurs.
In a critical digital procurement, an organization is not merely purchasing a system or a service. It is also procuring its future ability to act.
Identify Your Critical Digital Dependencies
Sigma Technology helps organizations in the public sector and operators of critical services to map systems, supplier dependencies, and security risks prior to procurement, modernization initiatives, and digital transformation.